SOCpedia Blog
RSyslog Templates (template): event formation and transformation.
Overview. Templates in RSyslog define in what form an event will be written to a file, sent to a remote server, or processed by another action. Using templates you can change the …
RSyslog Queues: Principles of Operation and Configuration Using NGINX Event Forwarding as an Example
General information. When forwarding logs to a remote server, you must account for the possibility that the server may be temporarily unavailable. To reduce the risk of losing eve…
Monitoring of Linux boot, reboot, and shutdown
1. Problem statement. As part of fulfilling regulatory requirements, it was necessary to prepare an evidentiary base for auditors regarding monitoring of Linux operating system bo…
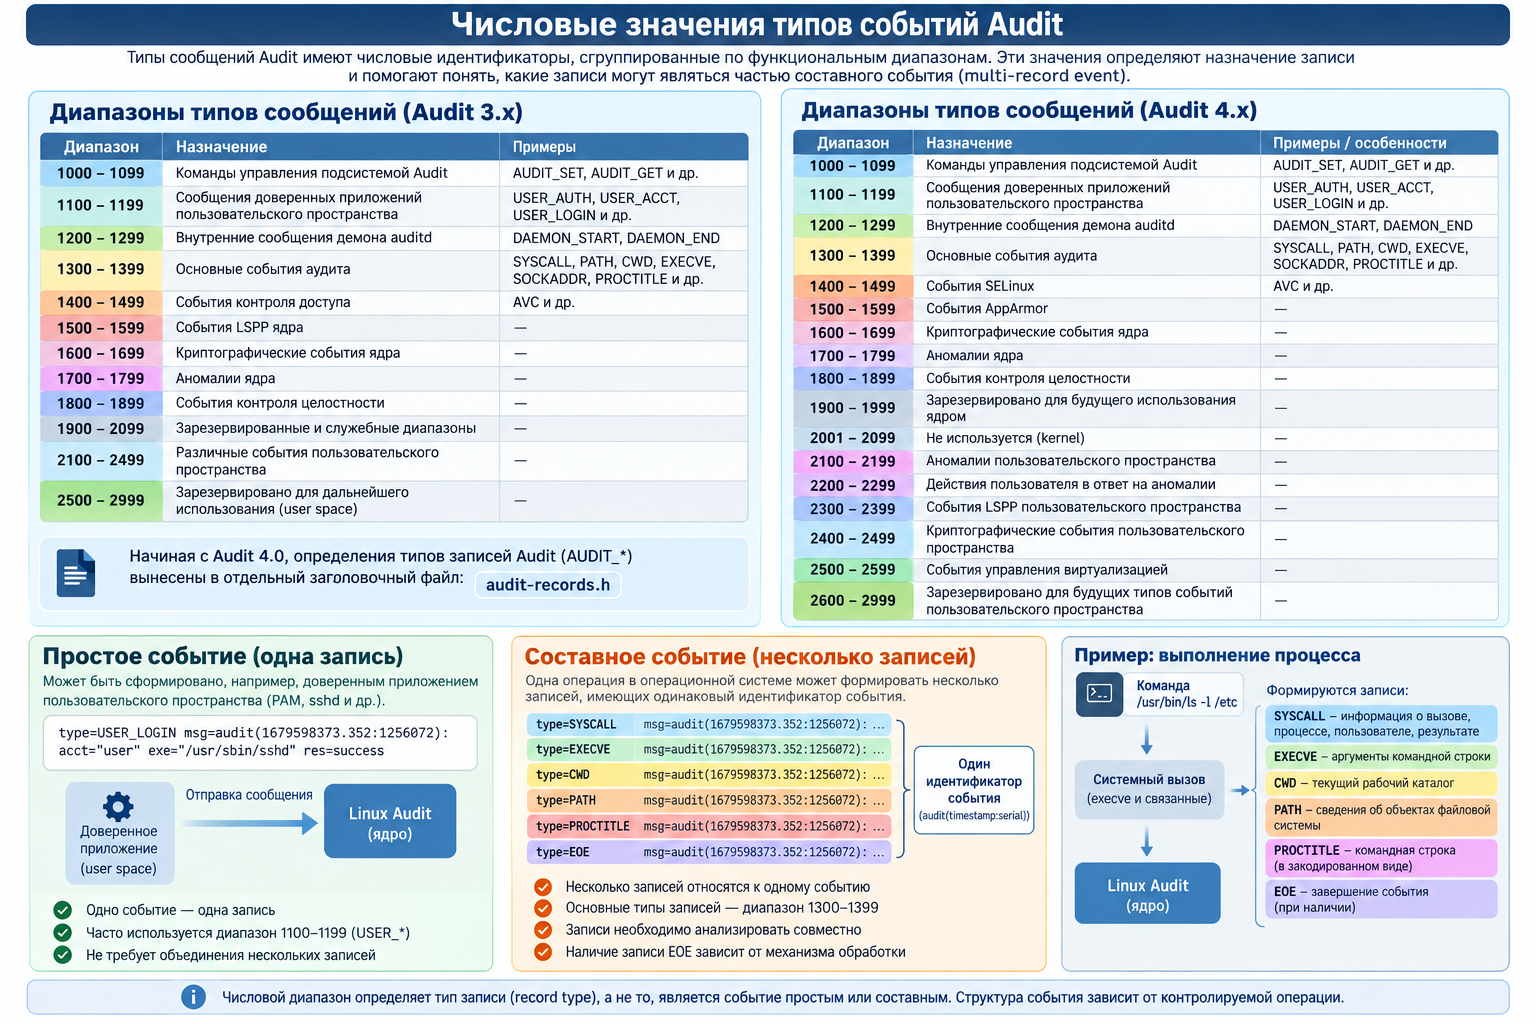
Numeric values of Audit event types
Audit message types have numeric identifiers grouped by functional ranges. These values are important not only for determining a record's purpose, but also for understanding which…
Basic description and architecture of auditd
1. Architecture overview. Linux Audit is an audit subsystem built into the Linux kernel, designed to record events related to the security of the operating system. It allows track…
Security Log Event 4741. How to Detect Suspicious Computer Account Creation in Active Directory
1. Legitimate activity. Event «A computer account was created» (A computer account was created) is generated on the domain controller each time a new computer object is created in…